Security Findings & Vulnerability Scanner
The Security Findings center (/sre/security) provides continuous automated vulnerability scanning for all container images, base operating system packages, application dependencies, and Kubernetes manifests running across your infrastructure.
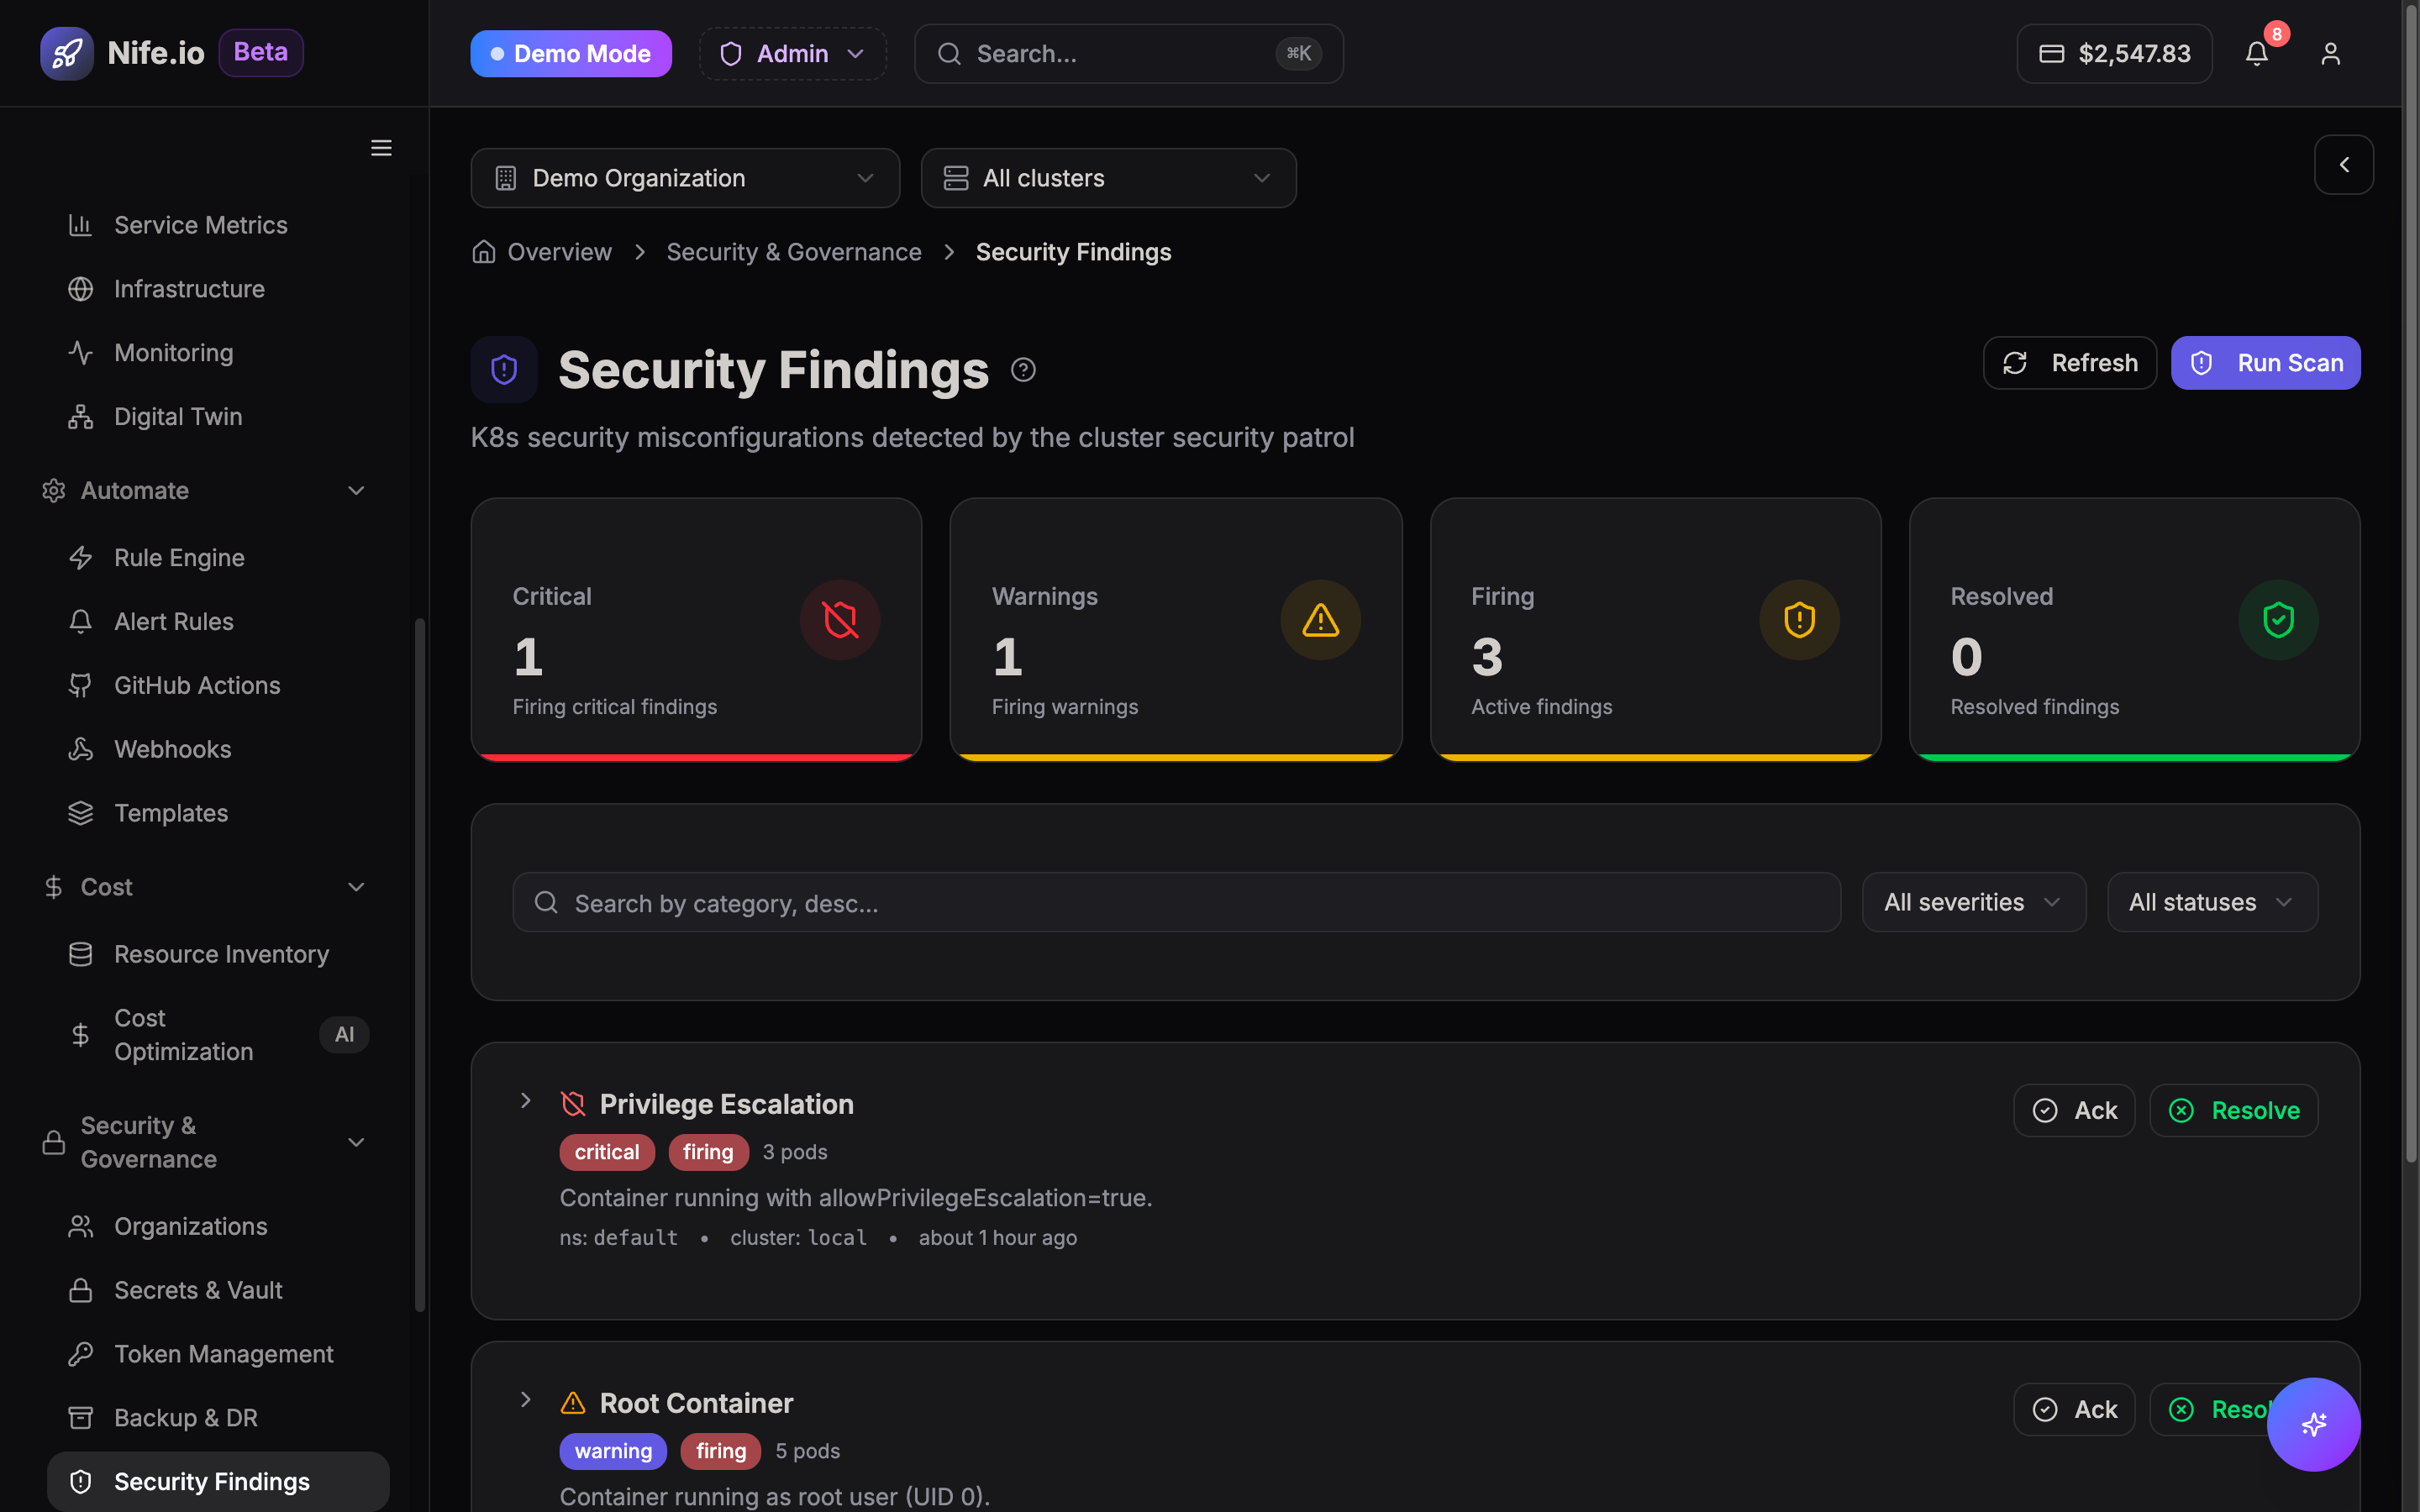
Security Findings Dashboard
The security findings dashboard categorizes open vulnerabilities by CVSS severity score, tracks remediation progress over time, and provides one-click patch recommendations.
Vulnerability Classification
Findings are categorized using standard Common Vulnerability Scoring System (CVSS v3) ratings:
| Severity | CVSS Score Range | SLA Recommended | Action Required |
|---|---|---|---|
| Critical | 9.0 – 10.0 | Immediate (24 Hours) | Remotely exploitable without privileges; upgrade base image or dependency immediately. |
| High | 7.0 – 8.9 | 7 Days | Significant exploit potential; apply available upstream vendor patch. |
| Medium | 4.0 – 6.9 | 30 Days | Moderate risk; schedule update in next sprint release cycle. |
| Low | 0.1 – 3.9 | Informational | Minimal attack surface; address during routine dependency refreshes. |
Key Security Features
1. Automated CI/CD & Runtime Image Scanning
- Pre-Deployment Gate: Scans container images pushed to connected registries (Docker Hub, GHCR, ECR) before scheduling pods.
- Continuous Runtime Scanning: Re-scans running workloads daily against newly published CVE databases (NVD, GitHub Advisory Database).
2. Software Bill of Materials (SBOM) Export
- Generate standardized SPDX and CycloneDX JSON/XML SBOM manifests for compliance and audit requirements.
- Inspect all installed OS packages (Alpine, Debian, Ubuntu, RedHat) and language libraries (npm, PyPI, Go modules, Maven).
3. Layer-by-Layer Root Cause Analysis
- Pinpoint the exact Dockerfile layer or base image dependency that introduced each vulnerability.
- View upstream fixed versions and direct upgrade commands.